Granular Roles & Permissions Governance
Enforce least-privilege access across every screen, branch, and data field.
Protect confidential margins, customer lists, and financial statements. Accurafin provides a robust Role-Based Access Control (RBAC) model allowing administrators to define fine-grained read, write, edit, delete, and export permissions across all organizational departments.
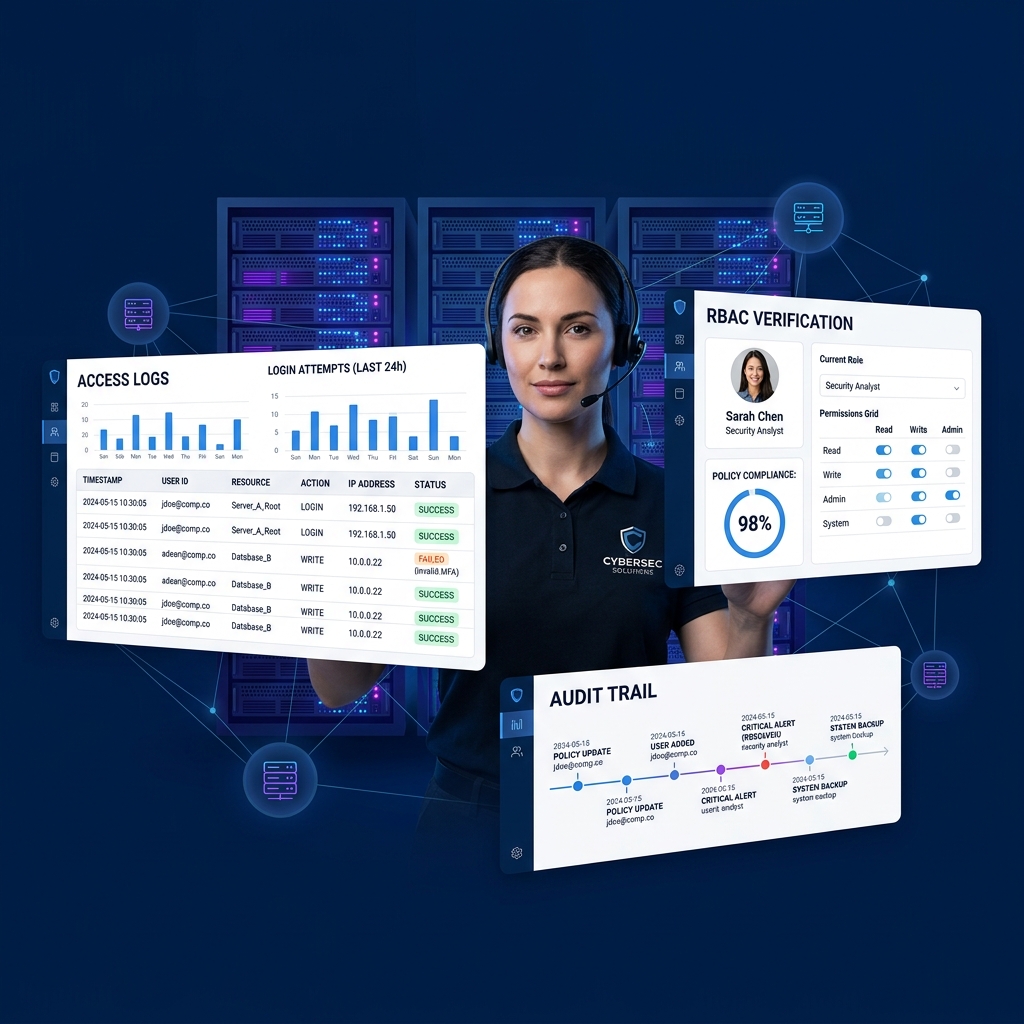
Strict Segregation of Duties and Data Confidentiality
Ensure that commercial employees only see the operational data required to execute their daily tasks.
Role-Based Permissions (RBAC)
Create unlimited custom user roles (e.g. Counter Cashier, Warehouse Picker, Sales Rep, Branch Accountant) with exact feature privileges mapped to job responsibilities.
Branch & Warehouse Scoping
Confine users to their assigned physical branches or warehouse locations. A store manager in Dubai cannot view customer quotations or stock balances belonging to Sharjah.
Field-Level Visibility Restrictions
Conceal sensitive operational figures. Hide cost prices and gross margin percentages on sales screens from junior sales staff, displaying only approved selling prices.
Segregation of Duties (SoD)
Prevent internal fraud by ensuring the user who prepares a purchase order cannot be the sole user who approves the supplier bill or issues the payment voucher.
Export & Print Control
Restrict customer list downloads, report exports to Excel, and document printing to authorized managers only, preventing unauthorized data exfiltration.
Session Management & 2FA Ready
Monitor active user sessions across devices, configure automatic inactivity lockouts, and enforce strong password policies across all team accounts.
Clear Delegation Without Operational Bottlenecks
Accurafin makes assigning permissions transparent. Managers can review the permissions matrix across modules to verify audit compliance at a glance:
- Create & Edit: Grant day-to-day transaction entry rights without granting ledger posting rights.
- Post & Finalize: Reserved exclusively for branch supervisors or certified accountants.
- Void & Delete: Locked behind strict supervisory review to prevent accidental or fraudulent record removal.
| Module / Function | Sales Rep | Storekeeper | Accountant |
|---|---|---|---|
| Create Quotations | Yes | No | Yes |
| View Unit Costs | Hidden | No | Visible |
| Post Goods Receipt | No | Yes | No |
| General Ledger Journal | No | No | Yes |
| Export Financials | No | No | Manager |
Strengthen access security and regulatory compliance
Schedule a personalized walkthrough demonstrating user role configuration, branch scoping, and field hiding.